HIPAA Has Two Parts
1- HIPAA Privacy – provides individuals with a legal & enforceable right to see and receive copies of PHI
2- HIPPA Security – requires physicians to protect patients’ electronically stored, protected health information (known as “ePHI”) by using appropriate administrative, physical, and technical safeguards
What does this mean for you? I get notifications from the HHS Office for Civil Rights (they manage HIPA enforcement), and there are two main things healthcare providers are being fined for
1- Not giving patients access to their PHI when they request it. (HIPAA Privacy)
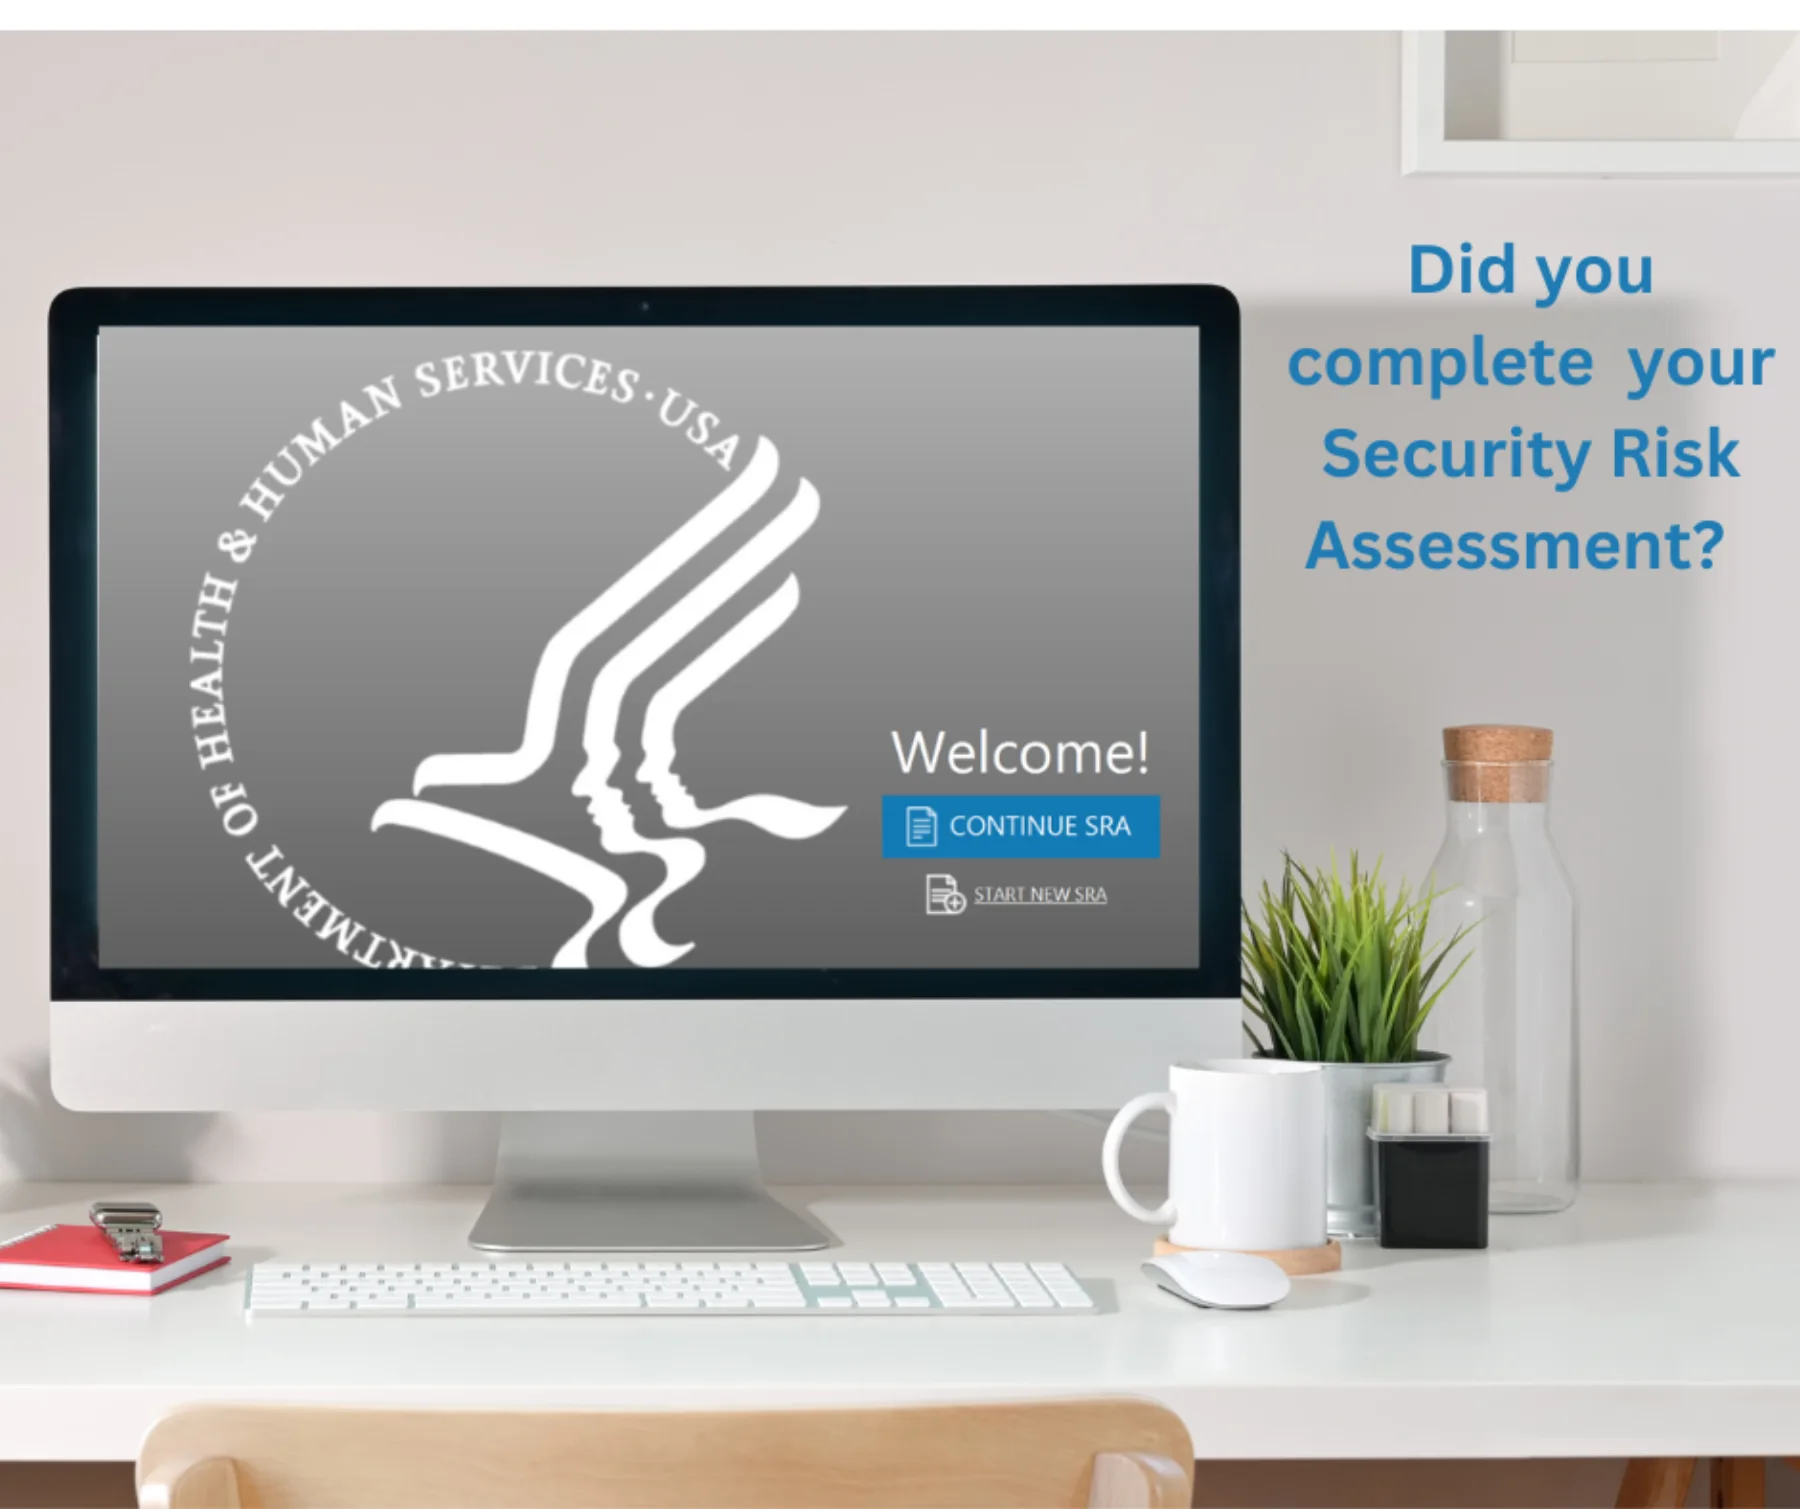
2- Not having completed a Security Risk Assessment. (HIPAA Security)
Being compliant with these is quite easy.
1- Have records request policies and procedures and follow them. This is as easy as requiring them to fill out a form that tells you what they are requesting and where it should be sent. Then the office sends the needed information promptly.
2- Back in the day, a Security Risk Assessment was very confusing and challenging to complete; a few hundred pages needed to be completed it was confusing and cumbersome. Now HHS has provided everyone with a free tool to complete the Security Risk Assessment (sometimes referred to as an analysis)
Need help? Breakthrough Coaching has resources to help you with both aspects of HIPAA.
1- We have a HIPAA complaint records request form and records request policies and procedures. BTC resource: Form 1167
2- Video instructions on how to easily complete a HIPAA Risk Assessment for the first time and update it annually in just minutes. BTC resource: AVM 950A-D